Electronic Signature Identity Verification
E-signature identity verification confirms who is signing before their signature is captured. TurboDocx does it with a one-time passcode by email or text, or by trusting the login your own app already runs, and writes the method onto the certificate of completion.
Key takeaways
- You pick how each signer proves who they are: an email passcode, a text message passcode, or the login your own app already trusts.
- The method is written onto the certificate of completion and the audit trail, so you can show an auditor how every signer was confirmed.
- Signers verified by your own identity provider get a short-lived link that opens once, so a forwarded link is useless.
- The signing page cannot be embedded on any website until your admin approves that site.
What is identity verification for electronic signatures?
Identity verification is the difference between a document that anyone with a link could sign and one where you can prove who actually signed. It confirms the signer before their signature is captured, then writes how they were confirmed into the permanent record of the document.
TurboDocx builds this directly into TurboSign, so the same platform that generates a document can verify the person signing it. You choose the level of assurance per signer, and nothing about the signer-of-record changes: they keep their real email address on the completed document.
How do you verify a signer's identity before they sign?
TurboDocx offers three ways to establish who a signer is, selectable per recipient. A one-time passcode by email or SMS covers most cases, and an assertion from your own identity provider covers signers already logged into your app. For development, a sender override lets you test embedded signing with no verification step; every signature it produces is marked as not identity-verified. The table below compares them.
Email OTP
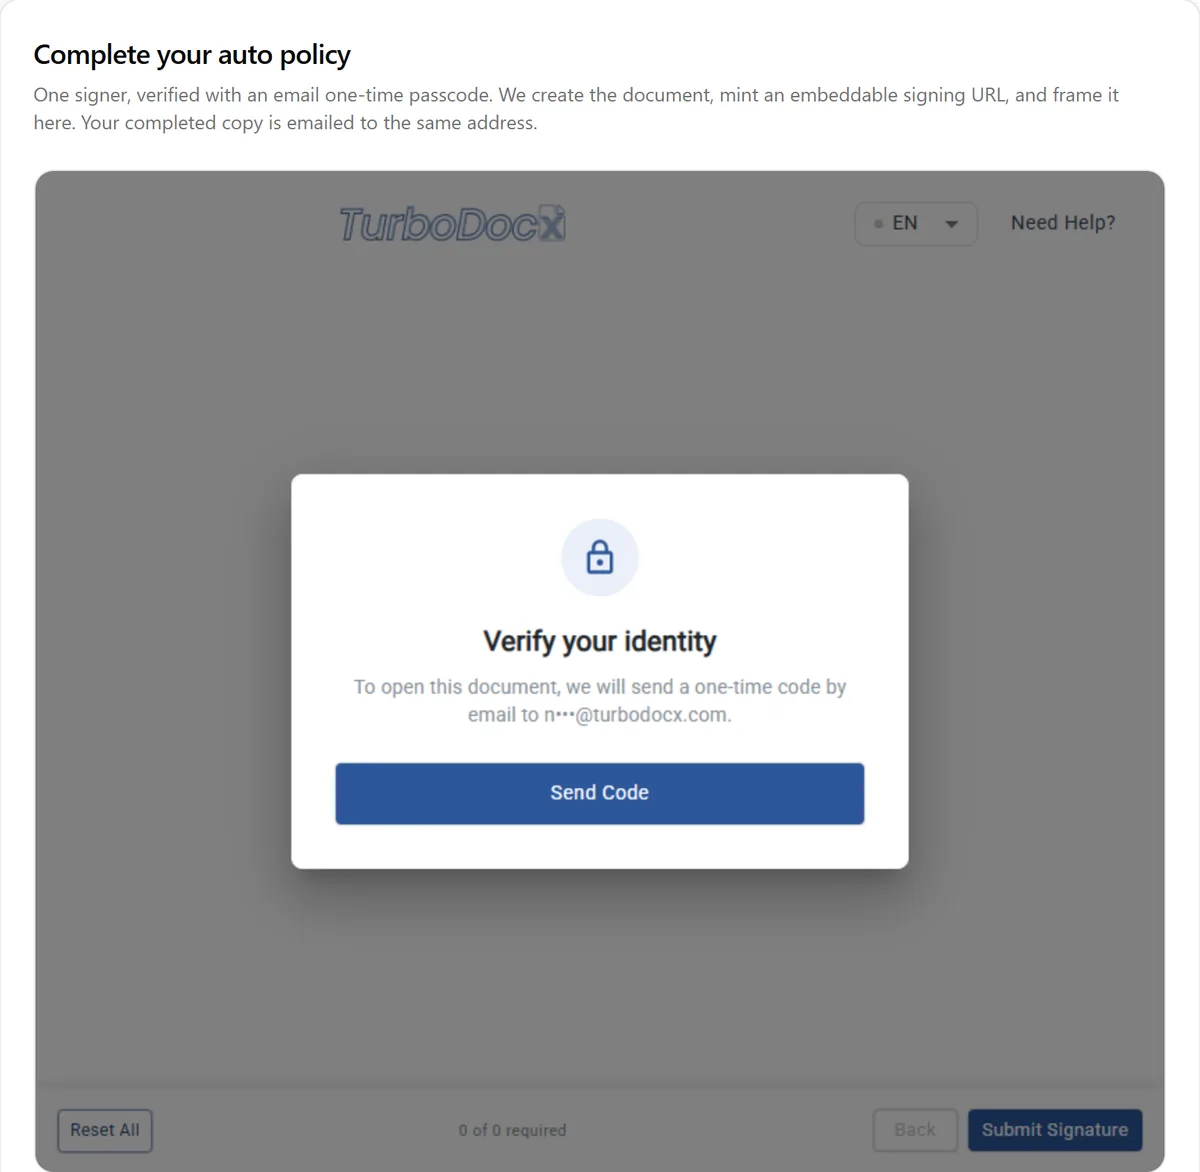
A single-use code is emailed to the signer, who enters it before the document opens.
SMS OTP
The same single-use code is texted to the signer’s mobile number instead of emailed.
External identity provider
Your app authenticates the signer through your own IdP or SSO and asserts that when it requests the signing URL.
Sender override (testing only)
Built for trying embedded signing without a passcode or an identity provider. It is not a way to verify a signer: an admin allows it, and the sender records a reason.
| Method | When to use it | What the signer sees | On the certificate |
|---|---|---|---|
| Email OTP | The default. Works for any signer with an email address and needs no phone number. | A "verify your identity" gate, a Send Code button, then a code entry field. | Recorded as email one-time passcode. |
| SMS OTP | Higher-assurance signers, or when email is untrusted. Needs a phone number and your own Twilio or RingCentral account. Pro and Enterprise plans. | The same gate, with the code arriving by text message. | Recorded as SMS one-time passcode. |
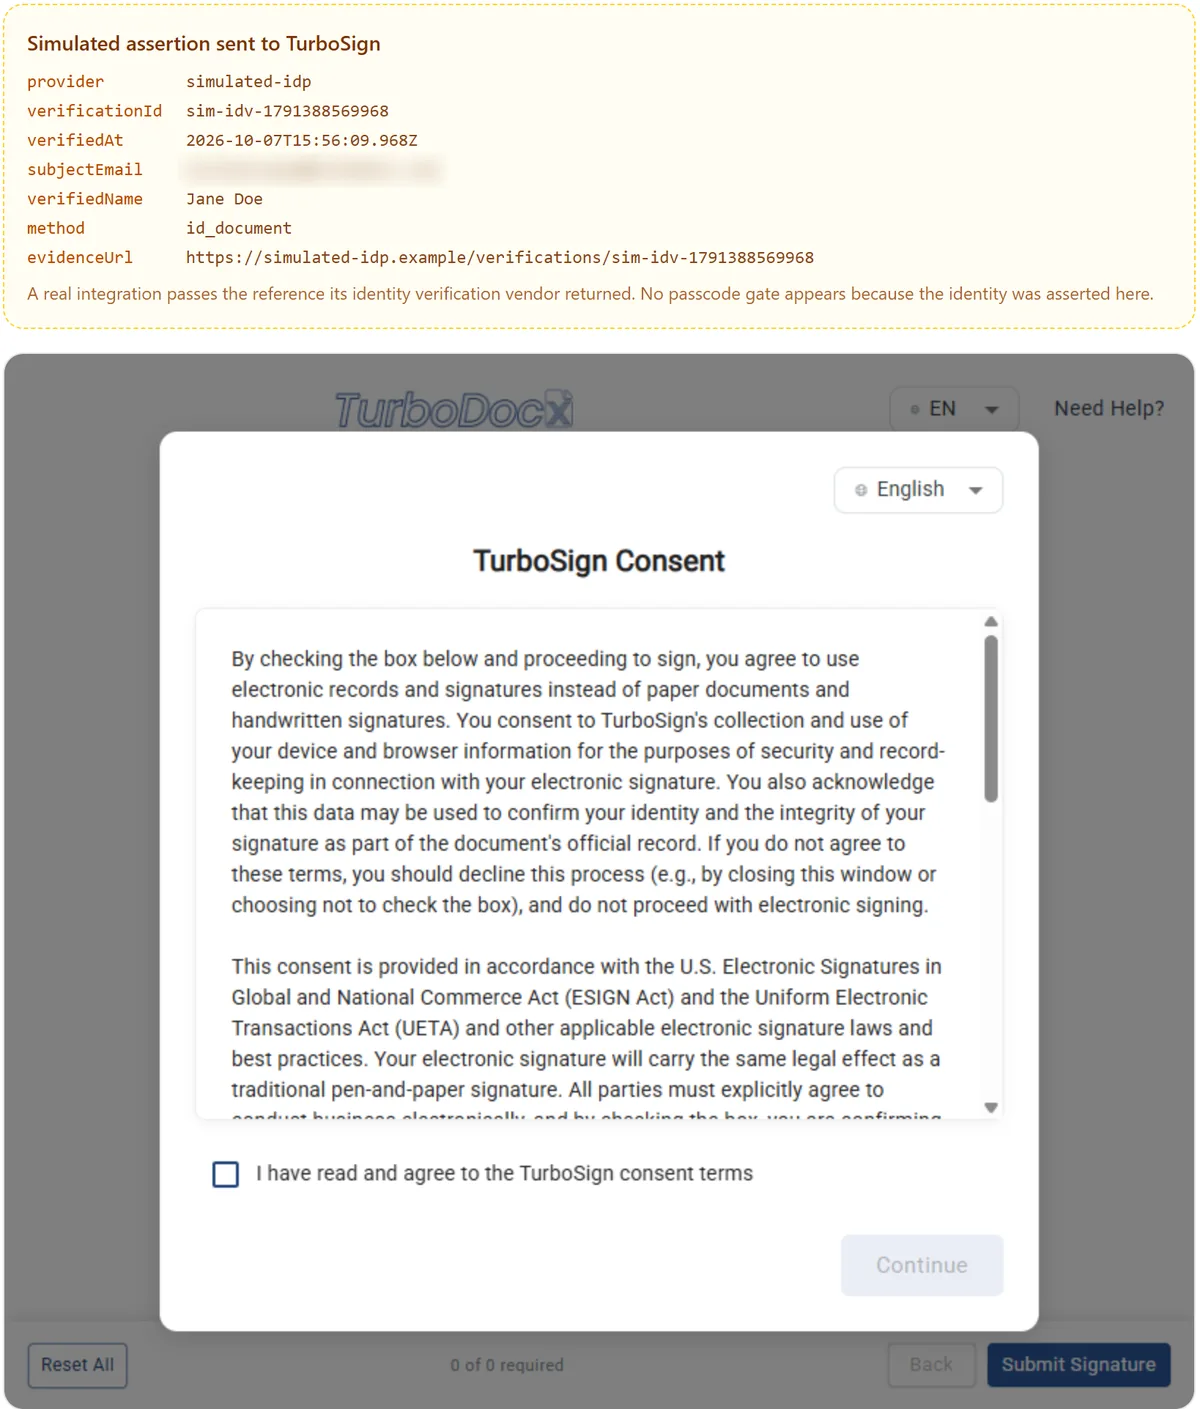
| External identity provider | You already know who the signer is because they are logged into your product. | No passcode step. The document opens straight away inside your app. | Recorded as external identity assertion. |
| Sender override (testing only) | Development and testing. Turn it off before you go live. An admin can keep it on in production if needed, and the marking still applies. | No passcode step. The document opens straight away. | Marked as not identity-verified, with the sender's reason recorded. |
How do you turn on identity verification in TurboDocx?
It is a few switches in one place. An organization admin opens Settings, Features and integrations, Configure E-Signature, then selects Identity Verification.
- On the One-time passcode tab, turn on Enable identity verification and choose when signers verify: only when a sender or an API request asks for it, or on every signature request. Turn on Allow SMS as an alternative to email and connect your own Twilio or RingCentral account if senders should be able to text the code.
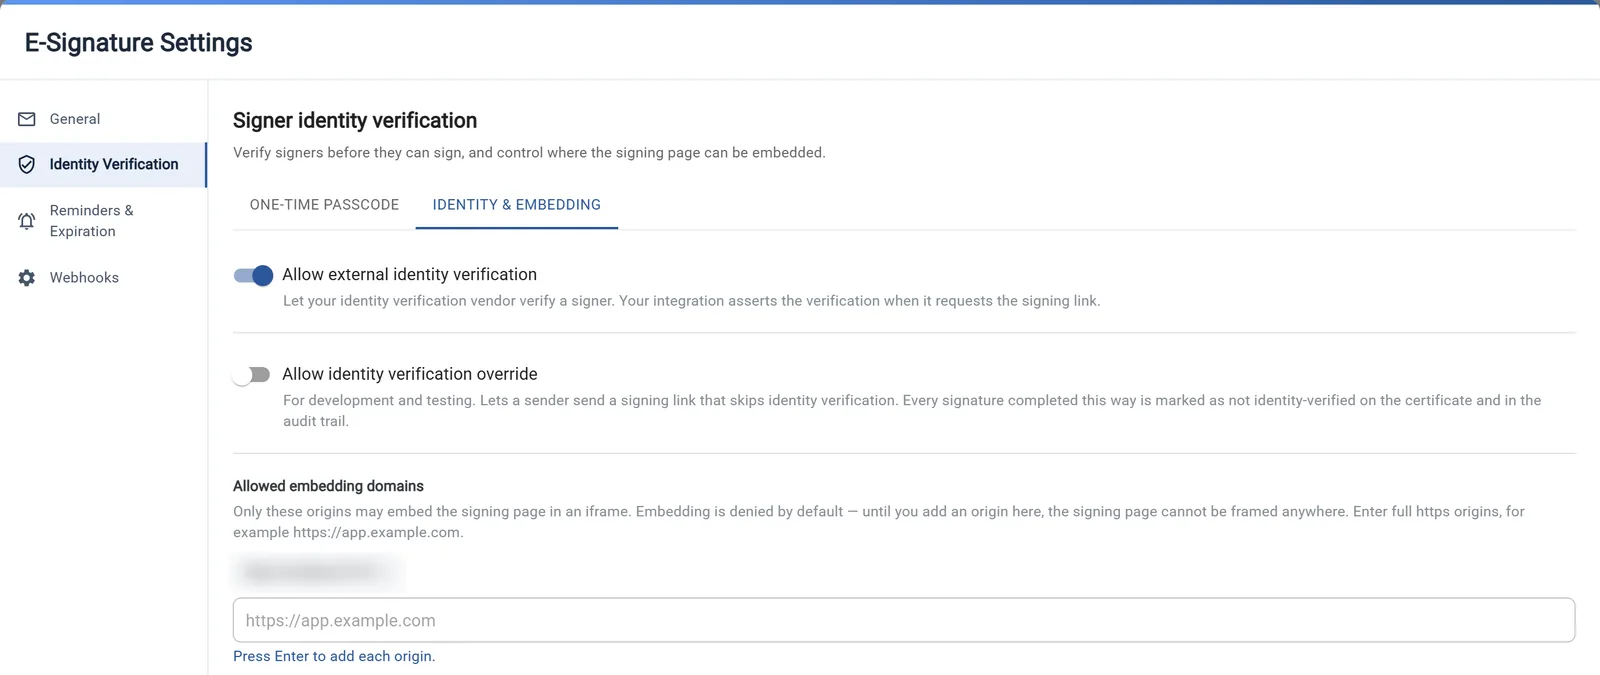
- On the Identity & embedding tab, turn on Allow external identity verification if your app will assert signers verified by your own provider. Leave Allow identity verification override off unless you are testing, because every signature that uses it is marked as not identity-verified.
- On the same tab, add each https origin that will frame the signing page to Allowed embedding domains. The list starts empty, so embedding is denied until you add one.
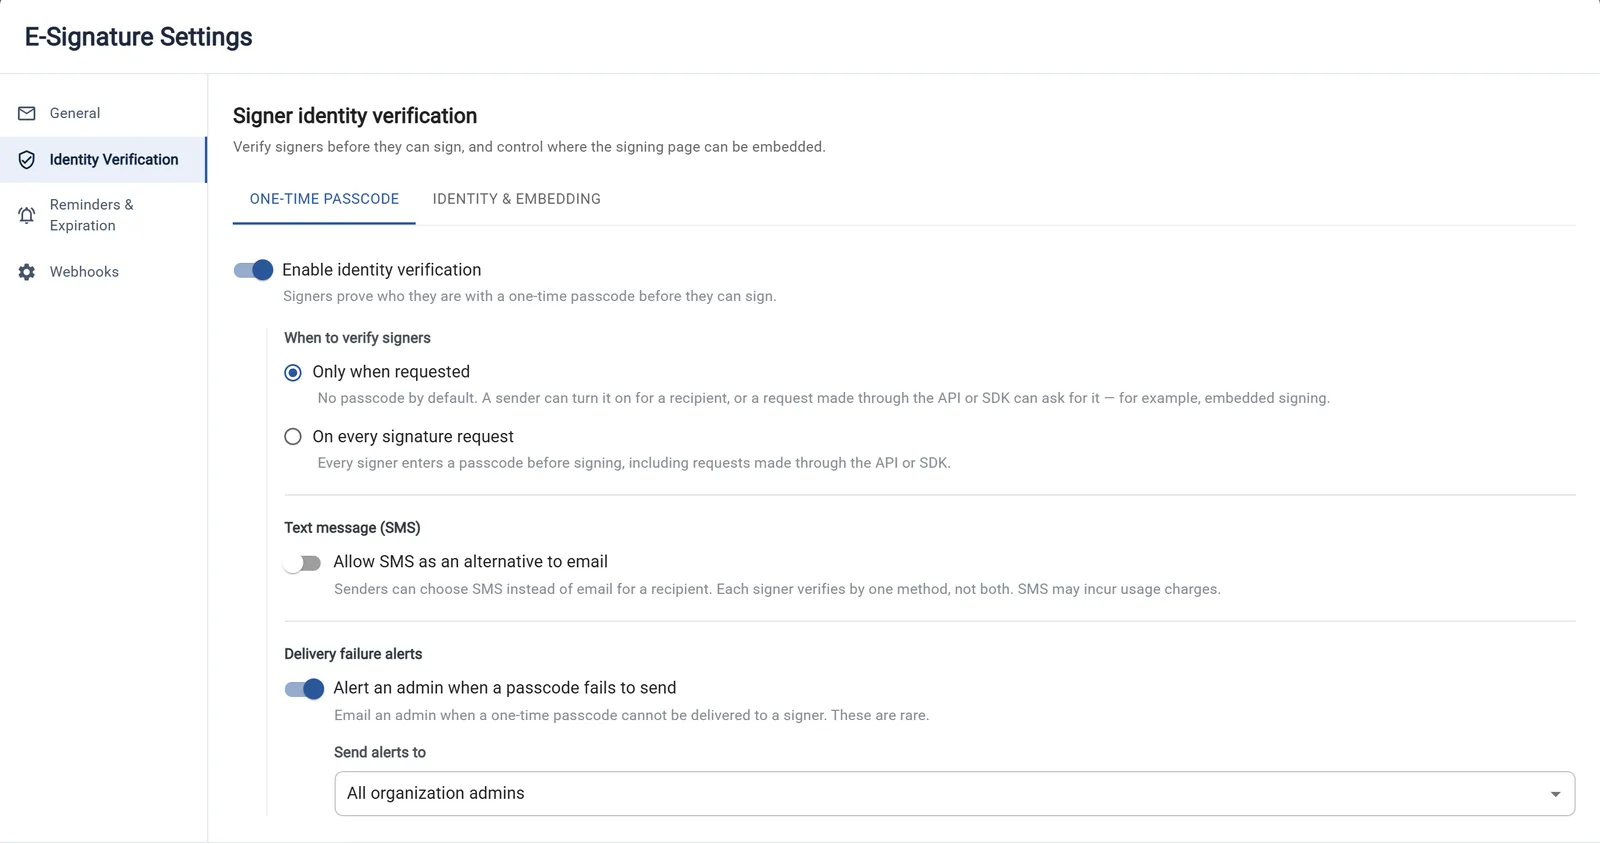
Email OTP vs SMS OTP: what's the difference?
Both deliver a single-use one-time passcode that the signer enters before the document opens. Email OTP sends the code to the signer's email address and works everywhere. SMS OTP texts the code to a mobile number, which is harder to reach from a compromised inbox but needs a phone number for the signer, and an admin must allow SMS and connect your own SMS provider in the E-Signature settings. Pick email for reach, SMS for a higher bar on out-of-band delivery.
Bring your own SMS provider
How do SMS passcodes work with your own Twilio or RingCentral account?
TurboSign does not text your signers from a shared number. An admin connects your organization's own Twilio or RingCentral account in the E-Signature settings, and every SMS passcode goes out from your number, on your account, billed by your provider at your rates. Signers see a number they can recognize, and the message logs live in your own provider account. SMS passcodes are available on Pro and Enterprise plans.
You connect: Account SID, Auth Token and a From number on that account.
Use a paid production account. Trial accounts block the custom message text a passcode needs.
Sending to US numbers also needs A2P 10DLC registration on your provider account.
Set it up in four steps
- 1
Pick your provider
On the One-time passcode tab, turn on Allow SMS as an alternative to email and choose Twilio or RingCentral.
- 2
Save your credentials
TurboSign checks the account straight away without sending a text. The status reads Connected when it is ready.
- 3
Send a test message
Text a number you control to confirm delivery end to end before a real signer depends on it.
- 4
Signers verify from your number
Senders choose SMS per recipient, or you make it the default for every signature request.
Every setting, status and provider check is in the email and SMS passcode guide.
Protection built into every code
- Cooldowns and send limits
- A signer can ask for a new code every 30 seconds, and no more than five times in a rolling hour.
- Lockout after repeated failures
- Each code expires in 10 minutes. After 20 wrong codes the signer is locked out until the sender resends the request.
- Alerts when a code cannot be delivered
- Your admins, or the addresses you choose, get an email so someone can help the blocked signer. On by default.
Email is always ready
Email passcodes work on every plan with no setup and arrive in a branded TurboSign email. If you remove your SMS credentials while SMS is the default, the default switches to email so signers can still verify.
Emails and texts follow the document's language or your organization's default:
- English
- Español
- Français
- Português
Can I verify signers with my own identity provider?
Yes. When a signer is already authenticated inside your product through your own identity provider or single sign-on, a passcode is redundant. Once an admin turns on Allow external identity verification, your backend asserts that verification at the moment it requests the signing URL, and TurboDocx skips its own passcode step while still recording that the signer was verified externally. The bring your own identity verification walkthrough lists every assertion field and check. This is the natural fit for embedded signing inside a logged-in app. Developers can wire it up with the e-signature API and the createSigningUrl guide.
Is a verified signer legally binding under the ESIGN Act and UETA?
A signature captured through TurboDocx is intended to be legally binding under the U.S. ESIGN Act and UETA, the same as any electronic signature we produce. Identity verification does not change that; it strengthens the evidence behind it by recording how the signer was confirmed. For the legal groundwork, see our guides on US e-signature compliance and how electronic signatures work.
Where is the verification method recorded?
On the certificate of completion and the audit trail for the document. Every signer's method, email OTP, SMS OTP or external identity assertion, is written into the signed record, so a reviewer, auditor, or opposing party can see exactly how each signer's identity was confirmed. A signature made with the testing override is marked as not identity-verified, with the sender's reason. Verification you cannot point to later is not worth much; TurboDocx makes it part of the evidence.
How is embedded signing kept secure across domains?
With a deny-by-default allow-list. No website can place the TurboDocx signing page in an iframe until you explicitly add its domain to your allowed embedding domains. The list starts empty, which means the signing page cannot be framed anywhere until you decide otherwise, closing the clickjacking gap that an open embed policy would leave.
The mechanics of requesting a signing URL and mounting it are covered on the embedded e-signature page and in the e-signature API reference.
What makes TurboDocx signer verification different?
Most e-signature platforms can authenticate a signer in some way. The difference is the combination: three ways to verify selectable per signer, a deny-by-default embedding policy, the verification method recorded on the certificate, the signer's real email kept as signer-of-record, and all of it in the same platform that generated the document. You are not stitching a signing tool to a separate identity tool.
- Email OTP, SMS OTP, or your own identity provider, chosen per signer
- Deny-by-default allowed embedding domains
- Verification method written onto the certificate of completion
- Signer keeps their real email as signer-of-record
- Generation and signing in one platform
- Developer-first API with an open-source core
Building at scale? Compare approaches for developers and legal teams, or send at volume with the bulk signature sending guide.
Frequently Asked Questions
What is identity verification for electronic signatures?
It confirms who a signer is before their signature is captured. TurboDocx can send a one-time passcode by email or text message, or accept the result of an identity check your own app already ran. For development there is also a sender override that skips verification so you can test embedded signing; every signature made with it is marked as not identity-verified. You choose the method per signer, the signer keeps their real email as signer-of-record, and the method that was used is written onto the certificate of completion and the audit trail.
What is the difference between email OTP and SMS OTP for signing?
Where the code is sent. The signer enters the same kind of one-time passcode before the document opens. Email OTP sends it to the signer's email address and needs nothing else. SMS OTP texts it to a mobile number, which keeps the code out of a compromised inbox, but it needs a phone number for the signer, and an admin must allow SMS and connect your SMS provider in the E-Signature settings.
Can I send SMS passcodes from my own Twilio or RingCentral account?
Yes. TurboSign sends SMS passcodes through your organization's own Twilio or RingCentral account, so texts come from your number and your provider bills them at your rates. An admin connects the account under Identity Verification in the E-Signature settings, TurboSign checks the credentials without sending a text, and a test message confirms delivery. SMS passcodes are available on Pro and Enterprise plans.
What happens if a signer never receives their passcode?
They can ask for a new code after 30 seconds, up to five codes in an hour. If a passcode cannot be delivered, TurboSign emails an alert to your admins, or to the addresses you choose, so someone can help the signer. After 20 wrong codes in total the signer is locked out until the sender resends the signing request.
Can I verify signers with my own identity provider instead of a passcode?
Yes. If your app already verified the signer, whether by ID document, liveness check or single sign-on, an admin turns on Allow external identity verification and your backend passes that result when it requests the signing link. TurboDocx skips its own passcode step, records your provider on the audit trail, and issues a link that opens once and expires within minutes.
Is a signature from a verified signer legally binding?
A TurboDocx signature from a verified signer is intended to be legally binding under the U.S. ESIGN Act and UETA, the same as any other TurboDocx signature. Identity verification does not change the legal basis; it strengthens the evidence by recording how the signer was confirmed. Our e-signature compliance guide covers the legal details.
Where is the verification method recorded?
On the certificate of completion and the document audit trail. Each signer's method, whether email OTP, SMS OTP, or an external identity assertion, is written into the signed record, so a reviewer, auditor, or opposing party can see how each identity was confirmed. A signature made with the testing-only sender override is marked as not identity-verified on both, and the sender's reason is recorded.
Verify every signer before they sign
Add identity verification to your signing flow in minutes. Start free, or see how the pieces fit on the pricing page.